
DDNS on an Industrial Router: A Name Is Not a Remote-Access Path

Updated: Oct 3
Dynamic DNS (DDNS) keeps a hostname associated with an address that may change. That is useful when an industrial site has a reachable WAN address, but it does not create a route through a carrier network or grant access to a PLC. Before configuring a DDNS client, check who needs to connect, which service they need, and whether the router can actually be reached from that network.
Understand What DDNS Changes
DNS maps a name to records such as an IPv4 A record or IPv6 AAAA record. A DDNS client notices the address to publish and updates the record through its provider's supported method. RFC 2136 defines one DNS dynamic-update protocol; many commercial DDNS services instead provide their own authenticated update API. Check the provider and the router's exact client implementation rather than assuming one method.


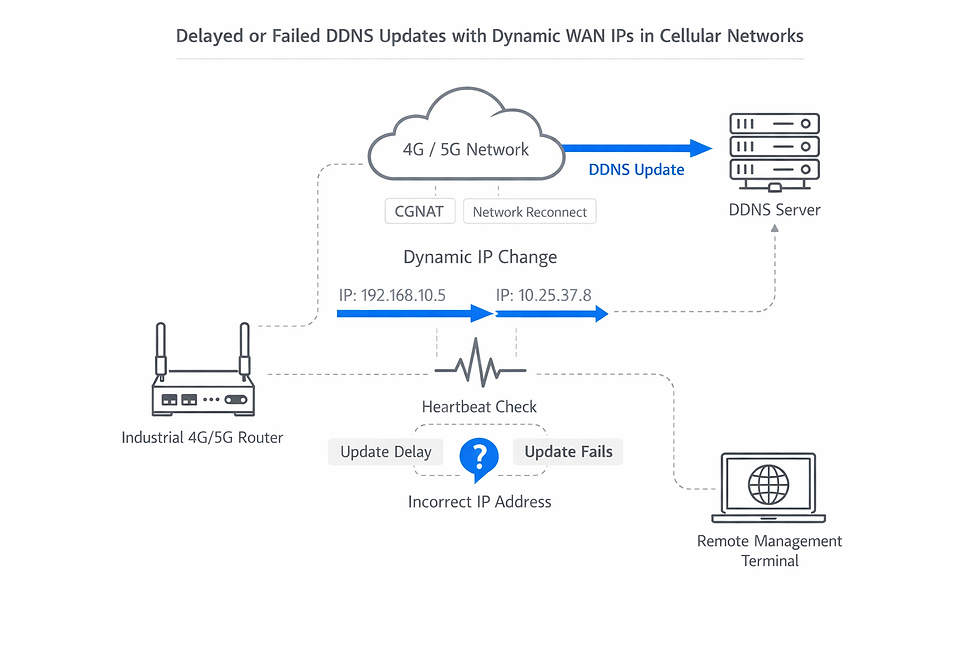


The update has several states: the router detects its current address, the provider accepts the change, authoritative DNS serves the new value, and resolvers stop using cached older values. A low configured TTL does not make every client change instantly. Record the address reported by the router, the published record and the address seen from the intended remote client.
Question | What to check | Why it matters |
|---|---|---|
Address | Public IPv4, global IPv6, private address or carrier-shared IPv4? | A hostname cannot make an unroutable address reachable |
Update | Which interface, account, authentication and interval are used? | A stale or incorrect record sends users to the wrong endpoint |
Name | Who controls the domain and update credentials? | A changed record can redirect maintenance traffic |
Service | Which VPN or application port is reachable under policy? | Correct DNS does not establish authorization or firewall access |
Check Cellular Addressing Before Inbound Access
Many cellular subscriptions use carrier-grade NAT (CGNAT). RFC 6598 defines shared IPv4 address space used between customer devices and carrier NAT. If the router reports a private or shared address while a public lookup reports a different address, a DDNS name pointing to the public address normally cannot establish a new inbound connection to the router without an operator-supported path.


Ordinary router port forwarding does not control the carrier's NAT.
Ask the operator whether the plan provides a public address, suitable IPv6 reachability, a private APN, or another supported access arrangement. If the remote engineer only needs maintenance, a router-initiated VPN to a controlled endpoint may fit better than exposing a management port. The remote PLC/HMI access guide starts from the actual user-to-device path.
Configure and Test the Whole Path
On the exact router model and firmware, confirm the supported DDNS providers, update source interface, credential storage and event log. Use a domain account with only the permissions required for the record. Protect the update channel according to the provider's method, and decide who rotates or revokes its token.
Test from outside the site network. Verify the name resolves to the intended address, then test the authorized VPN or service, the firewall boundary and the application task. Repeat after a WAN address change, SIM switch or power interruption. Measure how long the record, tunnel and application each take to recover. The failover guide explains why link recovery is not the same as session continuity.
If the name resolves but the session fails, inspect the address class, carrier policy, VPN listener, routes and firewall before changing DDNS settings again. If the name resolves to an old address, inspect client logs, provider response, authoritative record and resolver cache separately. Avoid publishing a public management interface merely to prove that the hostname works.
FAQ
Does DDNS give a cellular router a public IP address?
No. It updates a name-to-address record. The carrier's addressing and access service determine whether the router has an inbound-reachable path.
Will a correct DDNS record bypass CGNAT?
No. DNS resolution and carrier NAT are separate. Use a carrier-supported inbound arrangement or an outbound connection such as a suitably configured VPN.
Why does the old address appear after an update?
The client update may have failed, the provider may not yet serve the new value, or a resolver may hold a cached record. Check each stage and its timestamp.
Should the router's web administration be exposed through the DDNS name?
The name alone does not make that safe. Prefer a controlled remote-access design with authenticated users, limited services and audit records; verify the exact model's supported controls.


